OtterSec, Neodyme and Sec3 all publish Solana security work, but an auditor should be selected for the exact program architecture, scope and review team. Compare public reports, treatment of account and PDA invariants, upgrade authority, Token-2022 extensions, economic logic and remediation testing rather than assuming an EVM audit checklist transfers to Solana.

An RWA project on Solana can place issuance, permissions and settlement logic in programs while relying on off-chain records for investor eligibility or underlying assets. A generic smart-contract audit is not enough to evaluate this boundary. This comparison is for teams procuring a Solana program security review, not for choosing an EVM auditor by reputation alone.
Short Answer
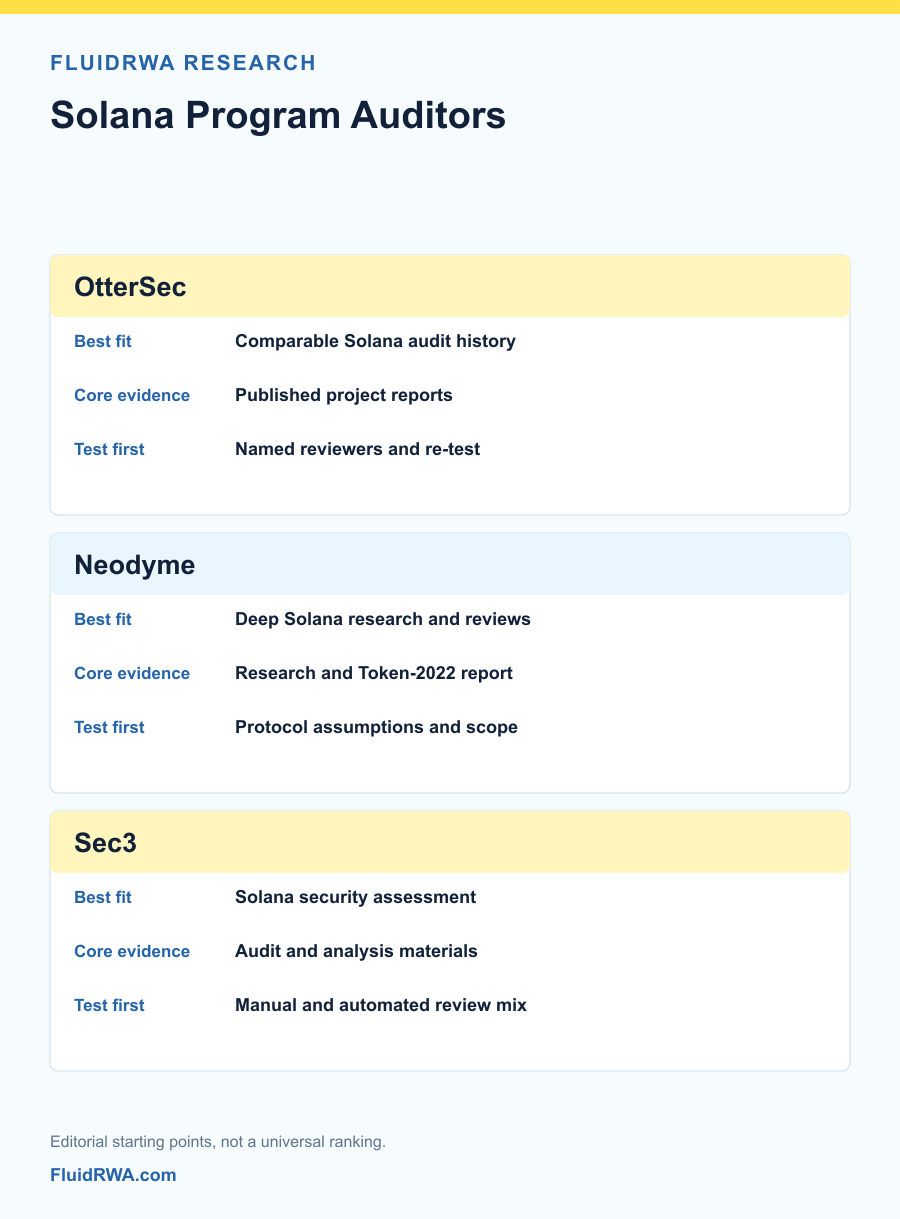
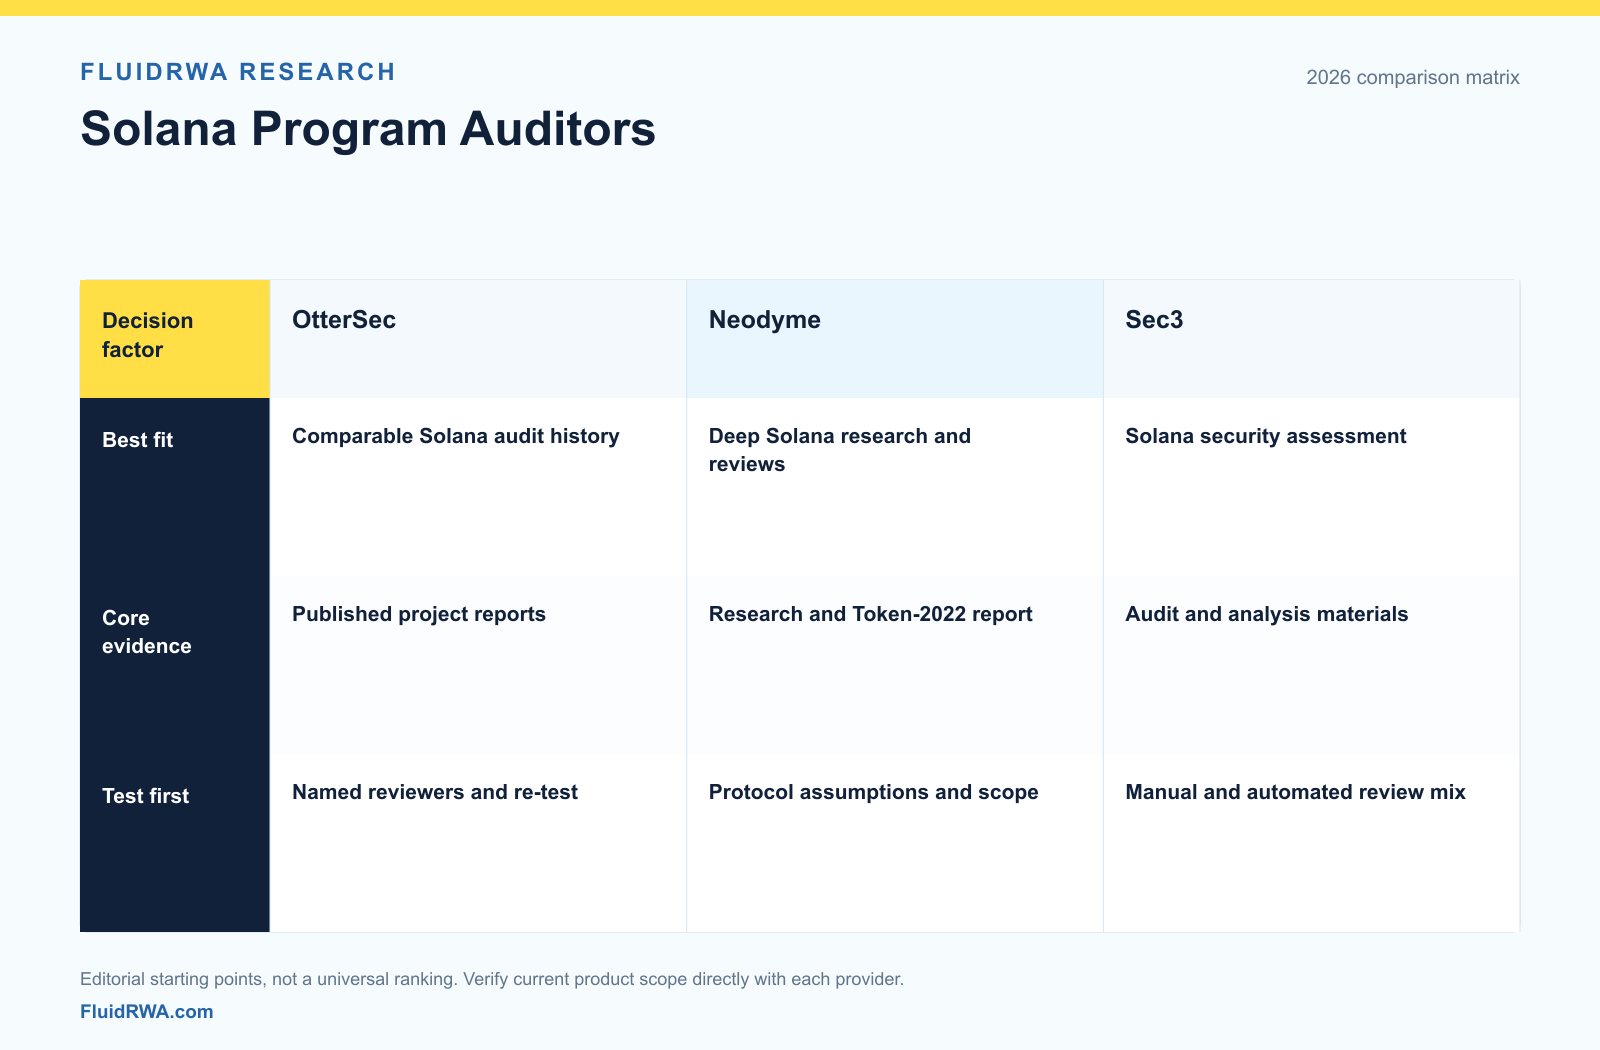
OtterSec, Neodyme and Sec3 are credible names to evaluate because each publishes Solana-focused work. The decisive question is whether the named team can review your architecture: account validation, PDA derivation, CPI boundaries, Token-2022 behavior, economic assumptions and privileged operations. Ask for a scoped plan and a sample report, then test the remediation process.
Comparison at a Glance
| Decision area | OtterSec | Neodyme | Sec3 |
|---|---|---|---|
| Public evidence to inspect | Published Solana audit portfolio | Solana research and audit reports, including Token-2022 | Solana audit and security materials |
| Best opening question | Which recent program is architecturally similar? | Which protocol-level assumptions will the review test? | Which analysis and manual-review steps are in scope? |
| RWA pilot focus | Issuance and permissions invariants | Token extension and account-model interactions | Static findings plus business-logic validation |
| Contract detail to confirm | Named reviewers and re-test terms | Scope, time allocation and report publication | Review deliverables and tool limitations |
Evidence, Not a Leaderboard
OtterSec's public audit list includes recent Solana programs. Compare the architecture and vulnerabilities in those reports with your own codebase rather than treating the number of projects as a quality score.
Neodyme describes Solana security research and audits and has published a Token-2022 review. That experience is relevant where extensions, token authorities or core-program interactions matter. It does not mean every feature of a buyer's application has been pre-reviewed.
Sec3 publishes Solana audit and security material. Ask how automated analysis, manual review, economic reasoning and post-fix validation are combined for the specific code and dependencies proposed.
Scope an RWA Program Correctly
The work order should enumerate deployed programs, commit hashes, dependencies, privileged accounts, upgrade authorities and off-chain trust assumptions. For a tokenized asset, include:
- Mint, burn and redemption permissions, including emergency paths.
- Allowlisting and transfer restrictions under both normal and failed KYC states.
- PDA seeds, signer checks, account ownership and account substitution risks.
- Token-2022 extensions actually enabled, not the entire standard by default.
- CPI calls to external programs and any assumptions about those programs' upgrades.
- Oracle inputs, pricing, collateral and settlement calculations where present.
- The boundary between on-chain token supply and the off-chain ownership or reserve ledger.
A Practical RFP and Test
Give each candidate the same architecture summary and a read-only code snapshot. Ask for a written review plan, effort estimate, named senior reviewer, exclusions, report-publication policy and re-test window. Request one worked example of a false positive or disputed finding and how it was resolved. After the audit, verify that fixes were tested against the exact production commit and that deployment keys and monitoring are separately controlled.
This page is deliberately narrower than the existing general security-audit comparison and security-auditor directory. It addresses Solana-specific procurement rather than repeating a broad ranking.
Primary Sources and Editorial Note
- OtterSec public audit portfolio
- Neodyme blockchain security work
- Neodyme Token-2022 report
- Sec3 Solana audits
This is independent procurement research, not a security certification. Report scope, availability, staffing and pricing must be checked directly with each firm.
FAQ
Can an Ethereum audit cover a Solana program?
No. Solana has different execution, account, authority and program-upgrade models. A team should commission a review specifically scoped to its Solana programs and dependencies.
Which auditor is best for Token-2022?
Neodyme has published a Token-2022 review, but historical work alone does not establish availability or fit. Ask all shortlisted teams to explain their experience with the exact extensions used.
What should an RWA issuer include in an audit?
Include issuance and burn controls, transfer restrictions, allowlisting, freeze and upgrade authorities, custody interactions, redemption state and off-chain reconciliation assumptions.
Does an audit make a program safe?
No. It reduces a defined set of risks within a scope and time window. Security also depends on tests, key management, monitoring, incident response and later code changes.
Scope the Solana review before asking for a quote
Share program code, dependencies, privilege model, deployment plan and threat assumptions with candidate auditors.