LayerZero documents configurable message verification and omnichain applications. Wormhole offers distinct products for native or wrapped transfers, messaging and queries. Axelar documents General Message Passing and Interchain Token Service. Compare the exact pathway, token supply controls, pause authority and recovery process for your deployment; this is not a security ranking.

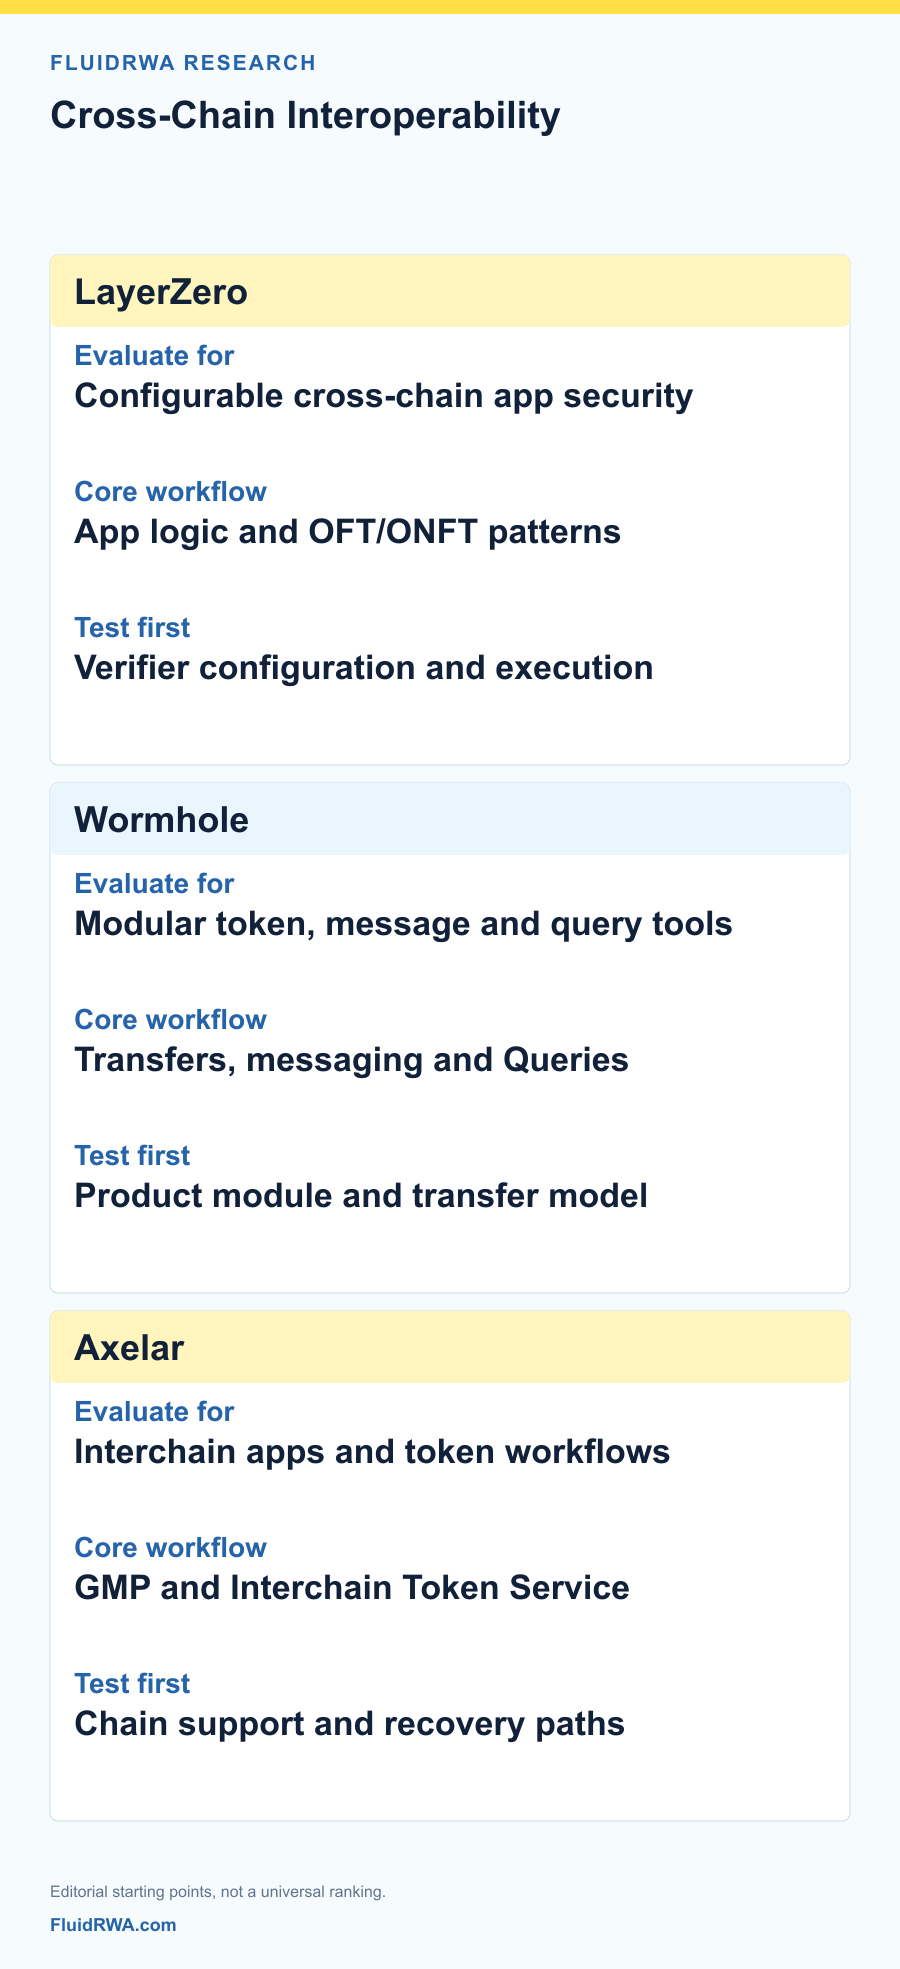
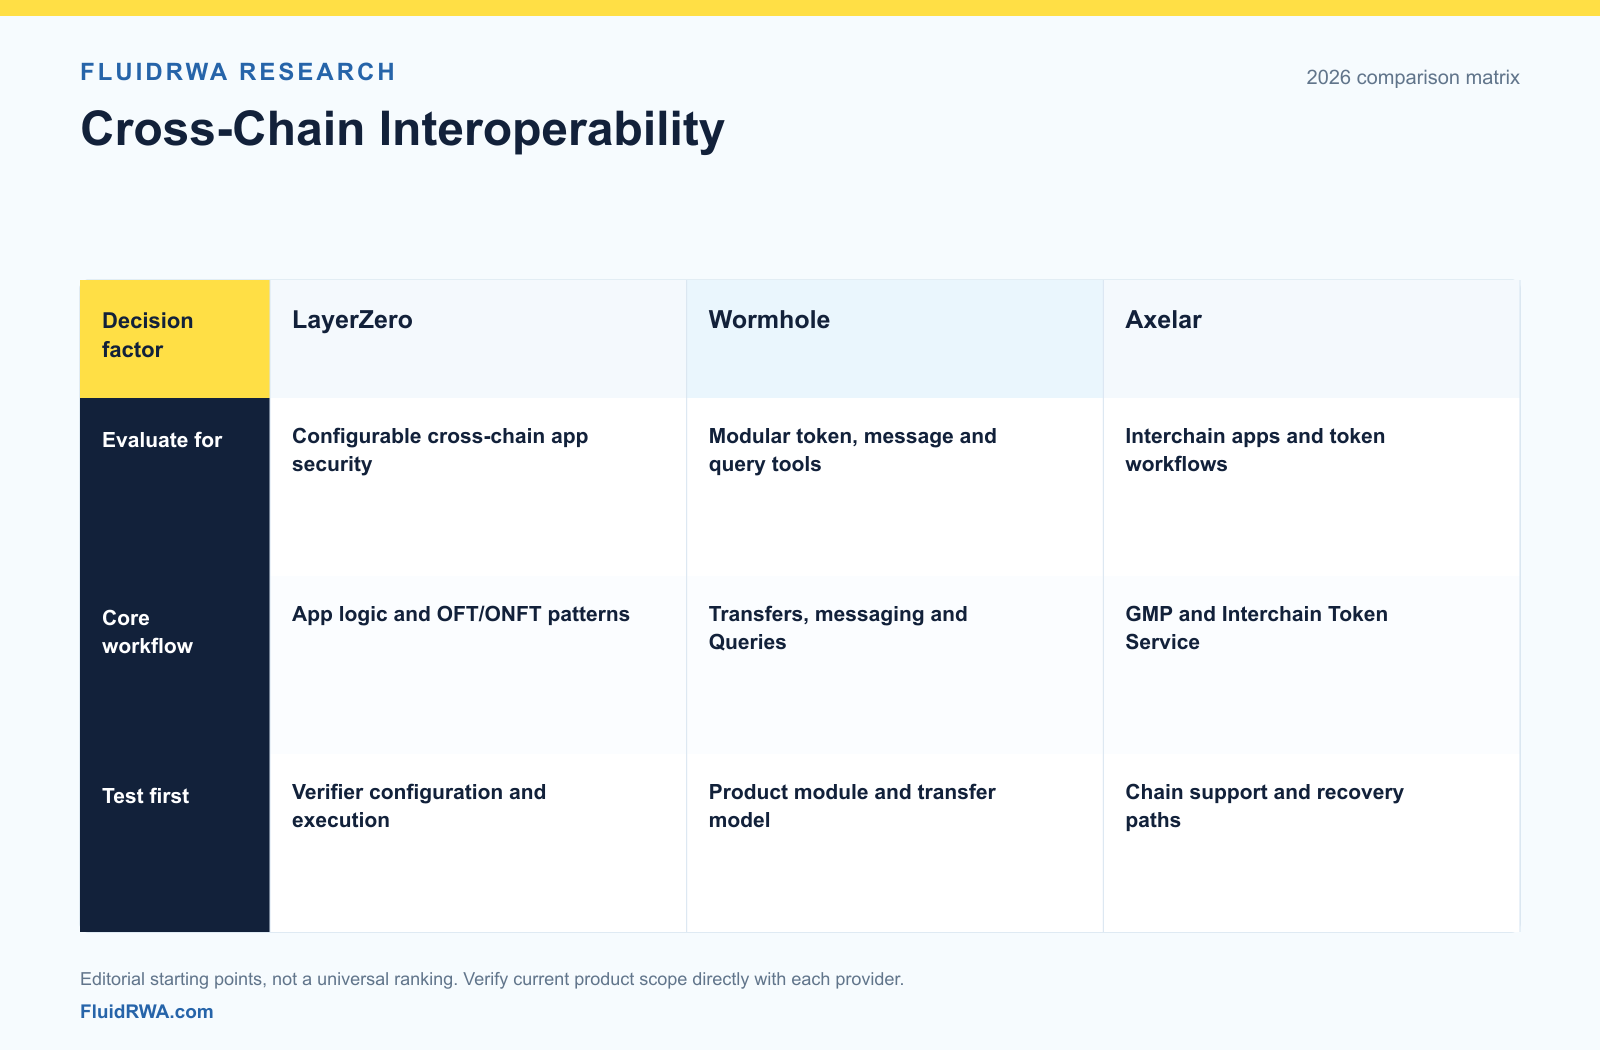
FluidRWA research brief
Cross-chain interoperability comparison snapshot
Interoperability is broader than bridging. Buyers should separate asset movement, messaging, state queries, governance, wrapped tokens, native token transfers and interchain application logic before choosing a vendor.
| Decision factor | LayerZero | Wormhole | Axelar |
|---|---|---|---|
| Natural buyer | Omnichain applications and teams needing configurable message security | Multichain apps needing modular transfer, messaging, query or governance products | Interchain apps and token projects needing message passing and interchain token support |
| Strongest workflow | Cross-chain app logic, OFT/ONFT-style patterns and configurable security | Native token transfers, messaging, Connect UI, Queries, Settlement and MultiGov | General Message Passing, Interchain Token Service and network-level interoperability |
| Best fit | Multi-chain tokenized products with app-specific message logic | Token or data movement across chains with modular tooling | Interchain token deployment and cross-chain product workflows |
| Main check before buying | How message verification and execution should be configured | Which product module fits the workflow and risk model | Whether the network and token model fits the supported chains |
A Token Move Has More Than One Step
The word "bridge" can hide the hard part. A transfer starts on one chain, has to be verified, then executed on another. If the last step fails, the issuer needs to know whether the token is still in flight and who can recover it.
That is why the comparison looks beyond supported-chain counts. Messaging, verification, token supply and administrative controls all affect what happens to a real asset.
For tokenized assets, the stakes are higher. A cross-chain mistake can affect investor records, transfer restrictions, canonical supply, reserve controls, market access or redemption operations.
LayerZero, Wormhole and Axelar are among the most visible interoperability providers, but they solve the problem with different architectures and product surfaces.
Short Answer
LayerZero is a strong fit when teams want to build omnichain applications with configurable security and cross-chain message logic.
Wormhole is a strong fit when teams want a modular cross-chain product suite: messaging, native token transfers, wrapped transfers, Connect, Queries, Settlement and governance tooling.
Axelar is a strong fit when teams want General Message Passing and interchain token workflows supported by its network and gateway architecture.
Compare the actual pathway
The provider name does not fully describe the security model. A production review should map one pathway from source-chain instruction to destination-chain execution:
| Layer | Evidence to collect |
|---|---|
| Source state | Contract address, event, finality threshold and replay protection |
| Verification | Named verifiers or validator set, quorum, diversity and upgrade authority |
| Delivery | Executor or relayer role, gas payment, retry logic and censorship fallback |
| Destination execution | Receiving contract, authorization checks and failure behavior |
| Token supply | Burn-and-mint, lock-and-mint or liquidity model, plus global accounting |
| Administration | Owners, pausers, rate-limit setters, upgrade keys and governance delay |
| Recovery | Monitoring, pause scope, in-flight message treatment and reconciliation |
Two integrations using the same protocol can have different risk because their configurations, contracts and administrative controls differ.
What to Test With Each Provider
LayerZero
LayerZero describes itself as an omnichain interoperability protocol. Its documentation focuses on sending messages, tokens and NFTs across many blockchains with configurable security, omnichain applications and endpoints deployed across supported chains.
LayerZero may be relevant when the buyer needs:
- omnichain application logic
- cross-chain messaging
- omnichain token or NFT standards
- configurable verification through DVNs
- a common app model across many chains
- user experiences where cross-chain complexity is hidden
LayerZero is relevant when the application itself needs to operate across multiple networks, not just move a token once.
The main diligence question is security configuration. LayerZero's production guidance explains that a single DVN can forge or suppress messages if compromised, while diverse multi-DVN configurations can reduce correlated failure. Buyers also need production confirmation depths, checks in both pathway directions and explicit executor and rollback choices.
Wormhole
Wormhole provides a suite of cross-chain products, including messaging, Native Token Transfers, Wrapped Token Transfers, Connect, Queries, Settlement and MultiGov. Its modularity is useful because not every cross-chain product has the same need.
Wormhole may be relevant when the buyer needs:
- plug-and-play bridge UI through Connect
- native token transfer flows
- wrapped token transfer workflows
- verified cross-chain messaging
- cross-chain data queries
- multichain governance
- modular tools rather than one fixed cross-chain path
For tokenized assets, Wormhole may be relevant where teams need asset movement, messaging, reporting or liquidity access across supported chains.
The main diligence question is which Wormhole product is actually being used. Current documentation distinguishes Native Token Transfers from Wrapped Token Transfers. NTT keeps issuer-controlled token contracts and supports controls such as rate limits and pausing, while WTT uses a lock-and-mint model with wrapped assets. Both rely on Guardian-signed messages.
Axelar
Axelar focuses on secure interchain communication and token transfers. Its materials describe General Message Passing, Interchain Token Service and a proof-of-stake network connecting multiple blockchains.
Axelar may be relevant when the buyer needs:
- general message passing between chains
- interchain token workflows
- cross-chain app calls
- decentralized network-level interoperability
- token deployment across multiple chains while preserving functionality
- cross-chain status visibility through explorers and tooling
Axelar is relevant for applications that want chain abstraction and interchain communication as part of the core product.
The main diligence question is whether Axelar's supported chains, token design, gateway administration and security assumptions match the product's financial risk. Buyers should also inspect rate limits, token-manager permissions and destination execution failure.
Comparison Table
| Decision factor | LayerZero | Wormhole | Axelar |
|---|---|---|---|
| Natural buyer | Omnichain applications and teams needing configurable message security | Multichain apps needing modular transfer, messaging, query or governance products | Interchain apps and token projects needing message passing and interchain token support |
| Documented workflow | Cross-chain app logic, OFT/ONFT-style patterns and configurable verification | Native token transfers, messaging, Connect UI, Queries, Settlement and MultiGov | General Message Passing and Interchain Token Service |
| Tokenization question | Can issuer rules be enforced on both chains? | Which transfer product and supply model would be used? | Who controls token-manager roles and destination execution? |
| Main buying question | How should message verification and execution be configured? | Which product module fits the workflow and risk model? | Does the network and token model fit our supported chains? |
| What to test | DVN configuration, message failure, supported chains and execution path | NTT/WTT model, Connect, Queries, monitoring and settlement behavior | GMP flow, ITS design, token behavior, explorer status and recovery paths |
Tokenized-asset control matrix
| Control | Why it matters |
|---|---|
| Canonical supply definition | Prevents multiple chain representations from being treated as independently issued assets |
| Per-chain and global rate limits | Reduces the blast radius of a compromised pathway or incorrect mint authority |
| Transfer eligibility | Ensures cross-chain delivery does not bypass investor, jurisdiction or wallet restrictions |
| Pause and unpause separation | Stops new movement without giving one role unchecked restart authority |
| In-flight transaction handling | Defines whether pending transfers complete, refund or require manual reconciliation |
| Supply reconciliation | Connects burns, mints, locked balances and outstanding messages to the authoritative record |
Multi-Chain Does Not Always Mean Better
Tokenized asset issuers should be careful with multi-chain launches. More chains can mean more distribution, but they also add:
- more smart contracts
- more monitoring surfaces
- more wallet support requirements
- more oracle dependencies
- more bridge or message risk
- more legal and compliance complexity
- more reconciliation work
- more incident response planning
Multi-chain makes sense when there is a concrete reason: investor access, liquidity, partner requirements, settlement rails or ecosystem distribution.
Buyer checklist
Before choosing LayerZero, Wormhole, Axelar or another interoperability provider, ask:
- Are we moving assets, messages, state, governance or all of them?
- Do we need native tokens, wrapped tokens or message-based actions?
- Which chains are required at launch?
- Which chains may be added later?
- What is the verification model?
- Who operates validators, guardians, verifiers or relayers?
- How are failures detected and retried?
- What monitoring exists for stuck messages?
- What audits cover the relevant contracts?
- What happens during a chain halt or reorg?
- Can compliance rules be enforced across chains?
- Can investor records stay accurate across networks?
Run a failure drill before launch
The proof of concept should do more than complete one successful transfer. Test a source-chain reorganization, destination execution failure, duplicate delivery, reached rate limit, paused pathway with messages in flight, unavailable executor, compromised administrator and reconciliation after a partial outage.
Record which party detects each condition, who may intervene and what evidence proves that supply and customer entitlements remain correct.
Practical Recommendation
Choose LayerZero if your main need is omnichain application logic and your team can own the pathway's verifier and executor configuration.
Choose Wormhole if your main need is modular tooling for transfers, messaging, queries or governance, and select explicitly between native and wrapped token models.
Choose Axelar if your main need is General Message Passing or Interchain Token Service workflows and its network and gateway model fits the mandate.
For tokenized assets, do not choose cross-chain infrastructure before defining the legal record of ownership. If the asset is regulated, the chain architecture must support transfer restrictions, investor records and compliance evidence.
Continue Your Research
- Compare tokenization platforms
- Compare smart contract development companies
- Compare security audit companies
- Submit cross-chain requirements
Primary and Authoritative Sources
- LayerZero V2 documentation
- LayerZero production DVN configuration
- Wormhole product comparison
- Wormhole token transfers
- Wormhole NTT security
- Wormhole Guardians
- Axelar developer documentation
- Axelar Interchain Token Service
FAQ
Which is better: LayerZero, Wormhole or Axelar?
It depends on the transaction path. Ask each provider to show how the proposed chain pair verifies, delivers and recovers a message, and who controls token supply on both sides.
Is interoperability the same as bridging?
No. Bridging usually means moving assets. Interoperability can also include messaging, state queries, governance, data transfer, application logic and cross-chain token standards.
Do tokenized assets need cross-chain infrastructure?
Some do. Cross-chain infrastructure may be needed when tokenized assets, stablecoins, investor wallets, liquidity or settlement flows operate across multiple blockchains.
What is the biggest risk in cross-chain infrastructure?
The biggest risks are verification compromise, contract or configuration errors, supply-accounting failures, message failure, privileged-role compromise and an untested recovery process.
Should RWA issuers launch on multiple chains?
Not by default. Multi-chain launch only makes sense if distribution, liquidity, investor access or settlement benefits justify the added security and operations complexity.
What should buyers test before choosing interoperability providers?
Test supported chains, message verification, finality assumptions, token standard, bridge flow, monitoring, incident response, contract audits, documentation and integration effort.
Can cross-chain providers support compliance controls?
They can support technical movement, but compliance depends on wallet screening, transfer restrictions, identity controls, legal structuring and policy logic built around the cross-chain flow.
Where can I compare more infrastructure vendors?
FluidRWA maintains directories for tokenization platforms, smart contract developers, custody, oracles, RPC and security providers.
Compare cross-chain infrastructure carefully
FluidRWA helps Web3 and tokenization teams compare interoperability, bridge, oracle, custody and security vendors by asset movement risk.